 how-to
How to Conduct an Internal ITAR Compliance Audit
Table of Contents
- Building the ITAR Compliance Checklist for Defense Contractors
- Step-by-Step: How to Conduct an Internal ITAR Compliance Audit
- Determining Internal Audit Frequency for Defense Trade
- Documentation and Record-Keeping Requirements for Audit Trails
- Supply Chain and Vendor ITAR Compliance Verification
- Export Control Compliance Software Tools for Audit Management
- Common Pitfalls in ITAR Compliance Audit Execution
- Frequently Asked Questions
Last Updated: September 21, 2026
Building the ITAR Compliance Checklist for Defense Contractors
An ITAR compliance audit is a structured internal review that tests whether a defense contractor's export controls, technical data handling, and record-keeping meet the requirements of the International Traffic in Arms Regulations. This guide breaks the process into practical phases that compliance teams can run.
The stakes are high. Non-compliance can mean lost licenses, debarment, and criminal exposure. A solid ITAR compliance checklist for defense contractors starts with four core areas:
- Registration and licensing records for every controlled item
- Technical data storage, marking, and access logs
- Personnel screening for foreign national access
- Supply chain and vendor verification files
Each item needs an owner, a review date, and a paper trail. That structure is what turns a checklist into evidence.
Step-by-Step: How to Conduct an Internal ITAR Compliance Audit
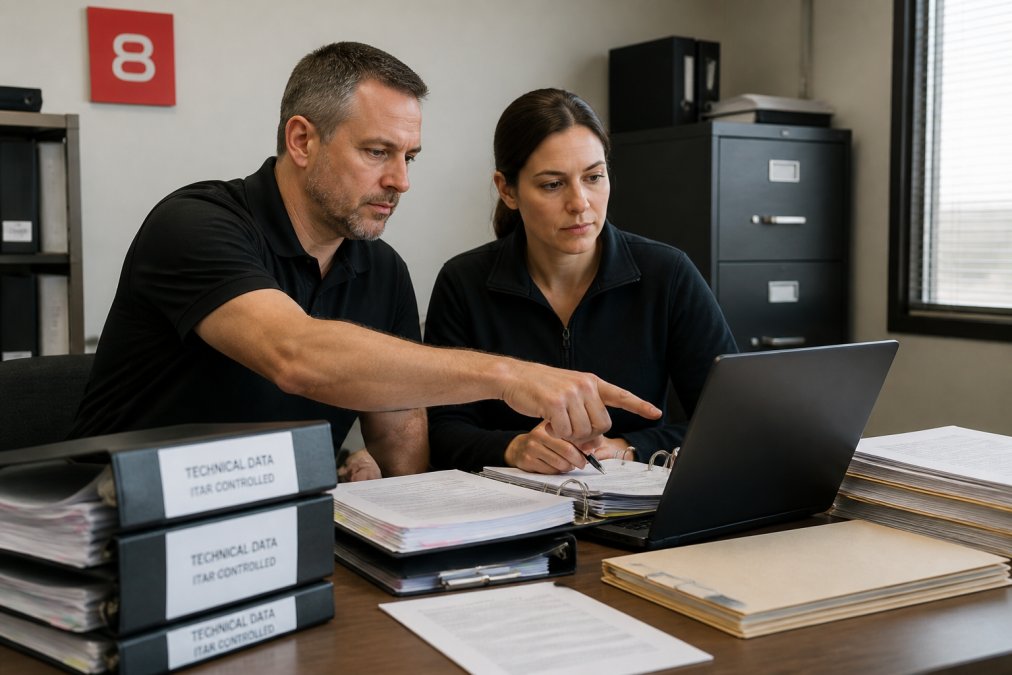
Running an internal ITAR compliance audit follows a repeatable sequence: scope the review, verify technical data controls, test records, check vendors, and document findings. The steps below map to a full audit cycle.
Phase 1: Scoping and Pre-Audit Preparation
Phase 1 defines what the audit covers and who runs it. A common mistake is scoping too wide and drowning in paperwork.
- List every ITAR-controlled program, product, and contract.
- Identify all staff who touch technical data.
- Pull the last audit's corrective action plan.
- Set a review window, usually 12 months.
- Assign an audit lead with authority to request records.
The audit lead should report to the compliance officer, not the program manager. Independence matters.
Phase 2: Technical Data Control Verification
Technical data control (TDC) verification is the part of an ITAR audit that generic compliance guides skip, and it is where most real findings surface. Under the ITAR, technical data is itself a controlled item, a drawing, a CAD file, a test procedure, or even a verbal briefing can be a deemed export if it reaches a foreign national without authorization. The audit test is not "is the file marked?" but "can you prove, from records, that every access was authorized?"
Run these tests in order, and record the result of each:
- Classification and marking. Sample at least 20 controlled documents across programs. Confirm each carries the correct ITAR legend (for example, the standard restricted-data statement) and that the legend matches the actual control status. A document marked "unclassified" that contains controlled technical data is a finding on its own.
- Access authorization. For each sampled document, pull the access list and reconcile it against personnel screening records. Every name on the list must have a documented basis for access, citizenship, a valid license or exemption, or an approved Technical Assistance Agreement (TAA) or Manufacturing License Agreement (MLA).
- Deemed export exposure. Check whether any foreign national employee, contractor, or visitor had logical or physical access to controlled data during the review window. Even inadvertent access counts. Verify that any such access was covered by an authorization, not assumed to be covered.
- Transmission and storage. Confirm that controlled data moves only through approved channels, encrypted systems, access-controlled repositories, and approved file-transfer tools. Email is the single most common failure point: a drawing attached to an internal message and forwarded outside the authorized group is a potential export, regardless of intent.
- Logs and retention. Verify that downloads, prints, shares, and repository access are logged with a timestamp, user identity, and document identifier. Logs must be retrievable for the retention period the regulations require. A control with no log is, for audit purposes, a control that did not operate.
A practical evidence standard: for each control, you should be able to produce a record that shows who did what, when, and under what authority. If you cannot, treat it as a finding and open a corrective action, do not explain it away.
Phase 3: Records, Vendors, and Findings
Phases 3 through 5, testing records, verifying vendors, and documenting findings, are covered in the sections that follow. Keep the same evidence standard throughout: a control is only as strong as the record that proves it operated.
Determining Internal Audit Frequency for Defense Trade
Internal audit frequency for defense trade depends on program size, data volume, and past findings. Most contractors audit annually, with quarterly spot checks on technical data.
Use this rule of thumb:
| Program Profile | Full Audit | Spot Checks |
|---|---|---|
| Small, single contract | Every 12 months | Twice a year |
| Multiple active licenses | Every 6-9 months | Quarterly |
| Prior violations found | Every 6 months | Monthly |
Programs with open remediation plans should audit more often until the corrective action plan closes. The goal is early detection, not a clean report.
Documentation and Record-Keeping Requirements for Audit Trails
An audit trail is the set of records that proves each control worked. Without it, a control does not exist as far as regulators are concerned.
Keep these records current:
- License applications and approvals
- Technical data access logs
- Personnel screening files
- Vendor and end-user verification documents
- Training completion records
Store records for the period the regulations require, and keep them retrievable. A folder nobody can find is not an audit trail.
Supply Chain and Vendor ITAR Compliance Verification
Vendor verification confirms that partners handling controlled items follow the same rules. Defense supply chains spread risk across every subcontractor, and an audit that stops at your own firewall will miss the largest exposure.
The ITAR mechanism that makes this auditable is the flow-down: when you pass controlled items or technical data to a subcontractor, the restrictions must travel with them through the subcontract.
- Registration status. Confirm the vendor is registered with the Directorate of Defense Trade Controls (DDTC) where registration is required, and that the registration is current for the period under review.
- Flow-down clauses. Pull the subcontract and confirm it contains the required ITAR clauses, including restrictions on re-export, re-transfer, and access by foreign nationals. A subcontract without flow-down language is a finding, even if the vendor behaved correctly.
- End-user and end-use statements. Obtain and review the end-user and end-use documentation for controlled items. Confirm the stated end use matches the authorization under which the item was exported or transferred.
- Technical data handling. Ask the vendor to demonstrate the same TDC controls you apply internally: marking, access authorization, transmission controls, and logs. Request a sample of their access records, not just a policy document.
- Personnel screening. Confirm the vendor screens personnel who will access controlled data, and that screening records exist for the review window.
- On-site checks for high-risk suppliers. For suppliers in higher-risk categories, those with foreign ownership, foreign national staff, or prior findings, schedule an on-site or remote walkthrough of their data controls.
Export Control Compliance Software Tools for Audit Management
Export control compliance software tools help teams log access, flag restricted parties, and store records in one place. The right tool cuts manual work and strengthens the audit trail.
Look for these features:
- Automated screening against restricted party lists
- Access control tied to personnel clearance
- Immutable logs for every technical data action
- Reporting dashboards for audit review
Common Pitfalls in ITAR Compliance Audit Execution
Most failed audits share the same mistakes. Avoiding them saves months of remediation.
- Treating the audit as a paperwork exercise. Controls must be tested, not just listed.
- Ignoring foreign national access. Personnel screening gaps are a top finding.
- Skipping vendor checks. Supply chain blind spots hide real risk.
- No corrective action plan. Findings without owners and deadlines repeat.
Frequently Asked Questions
What are the core components of an internal ITAR compliance audit?
An internal ITAR compliance audit covers five core areas: a documented ITAR compliance checklist for defense contractors, verification of technical data controls (including access logs and marking procedures), review of licensing and exemptions, supply chain and vendor due diligence records, and a corrective action plan for any gaps found. Each component must produce an audit trail that shows who reviewed what, when, and what was remediated.
How often should a defense contractor conduct an internal compliance audit?
Most defense contractors set internal audit frequency for defense trade at least once every 12 months, with additional targeted audits triggered by new contracts, changes in export control regulations, or personnel turnover in compliance roles. Companies with high volumes of technical data transfers or multiple international subsidiaries often run quarterly spot checks between full annual audits to maintain continuous regulatory oversight.
What documentation is required for an ITAR compliance review?
You need your current ITAR registration, a written compliance manual with standard operating procedures, records of all technical data transfers (including dates, recipients, and authorizations), personnel screening and training logs, vendor and supply chain due diligence files, and a corrective action plan from the last audit. Each document must be traceable to a specific regulatory requirement to satisfy enforcement scrutiny.
What are the consequences of failing an internal compliance audit?
Failing an internal audit means you have identified non-compliance before a regulator does. Consequences range from mandatory remediation and increased monitoring to civil penalties, loss of export privileges, or criminal liability for willful violations. The audit trail you create during a self-assessment is your strongest mitigation evidence if enforcement action follows, so document every corrective action plan step carefully.
Defense trade leaves no room for guesswork, and internal audits are where discipline shows. DIAGRAM8 brings a unified governance framework, multi-jurisdictional compliance, and audit-grade execution to complex cross-border engagements. With ISO 9001, ISO 27001, and ISO 37001 certifications behind its work, DIAGRAM8 gives institutional partners a confidential, ethics-driven path through regulated commerce. Request a formal introduction to DIAGRAM8 and put audit-grade discipline behind every deal.